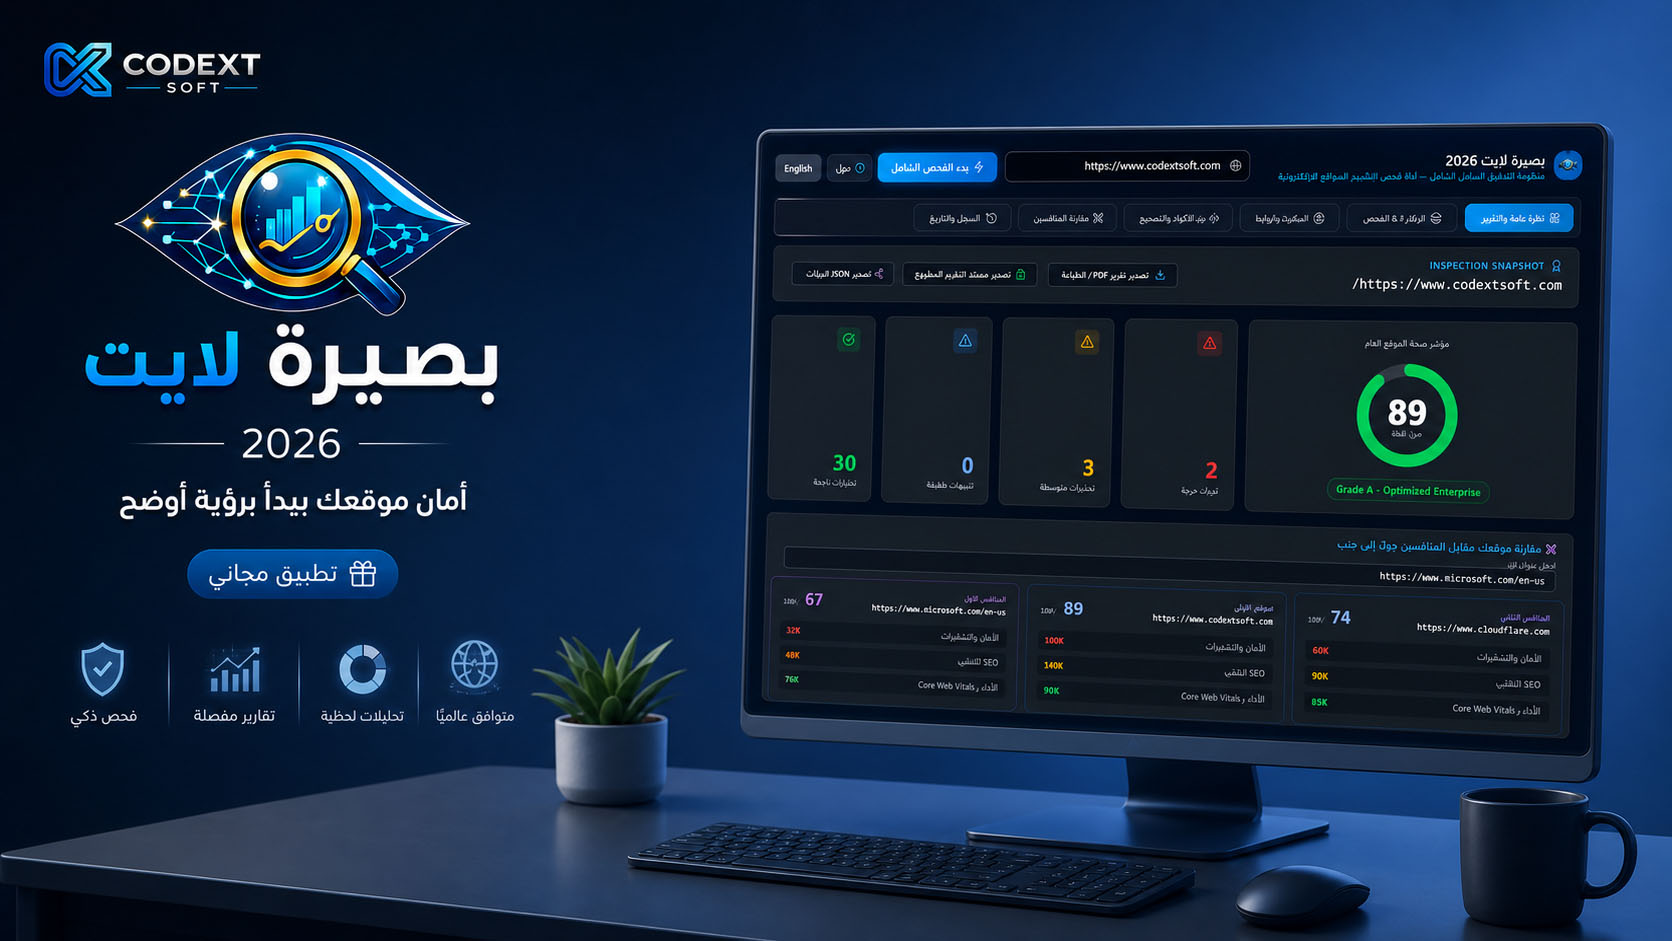
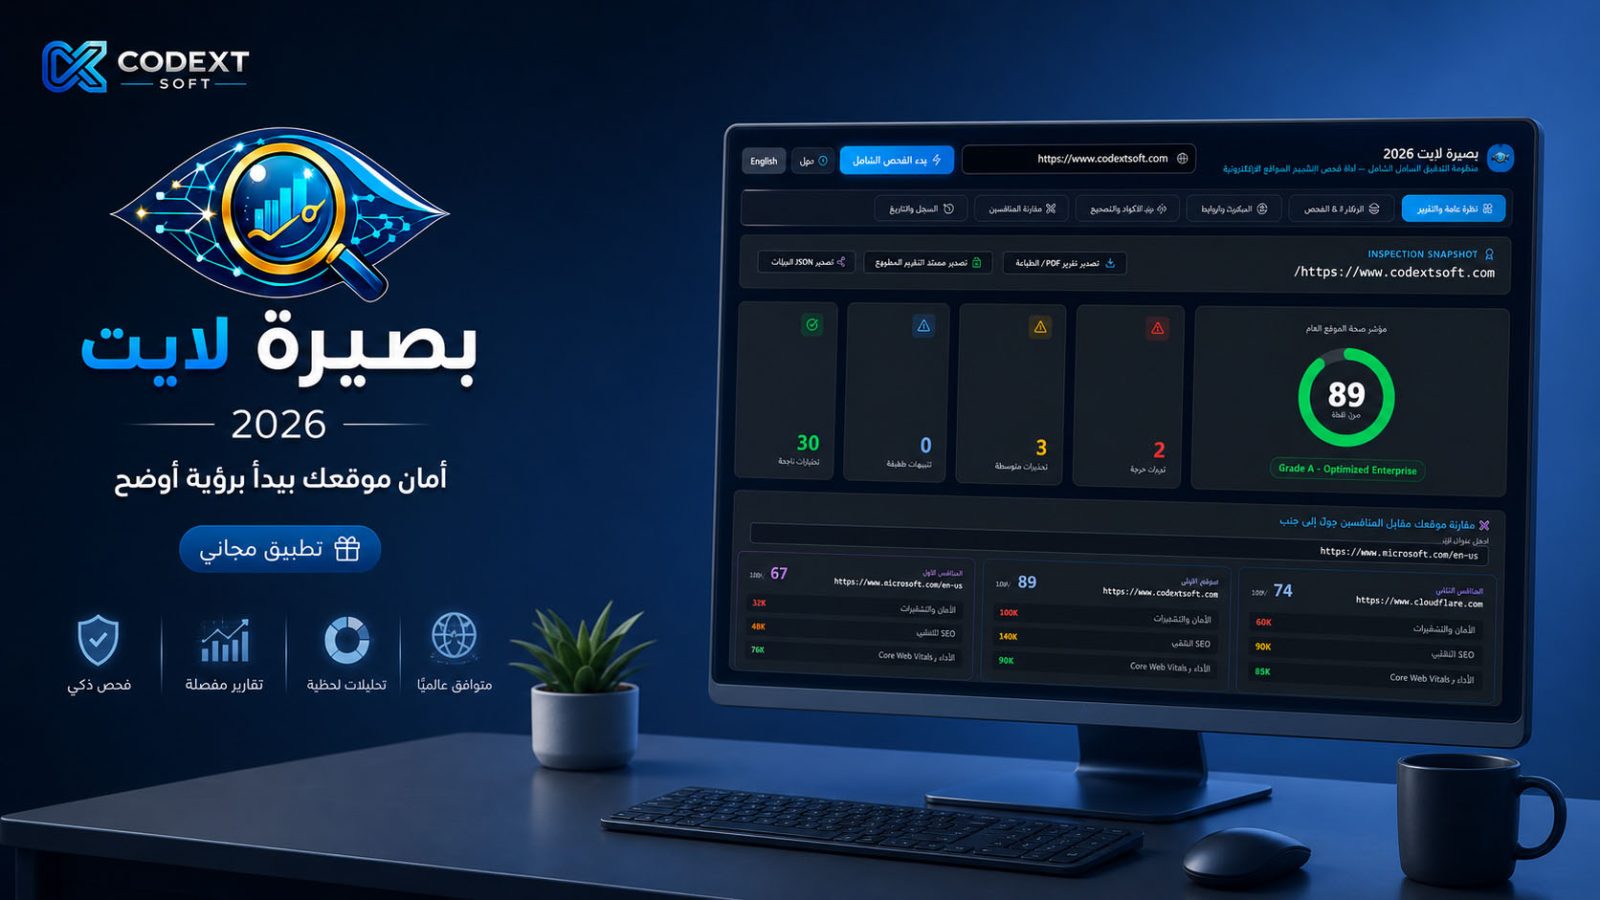
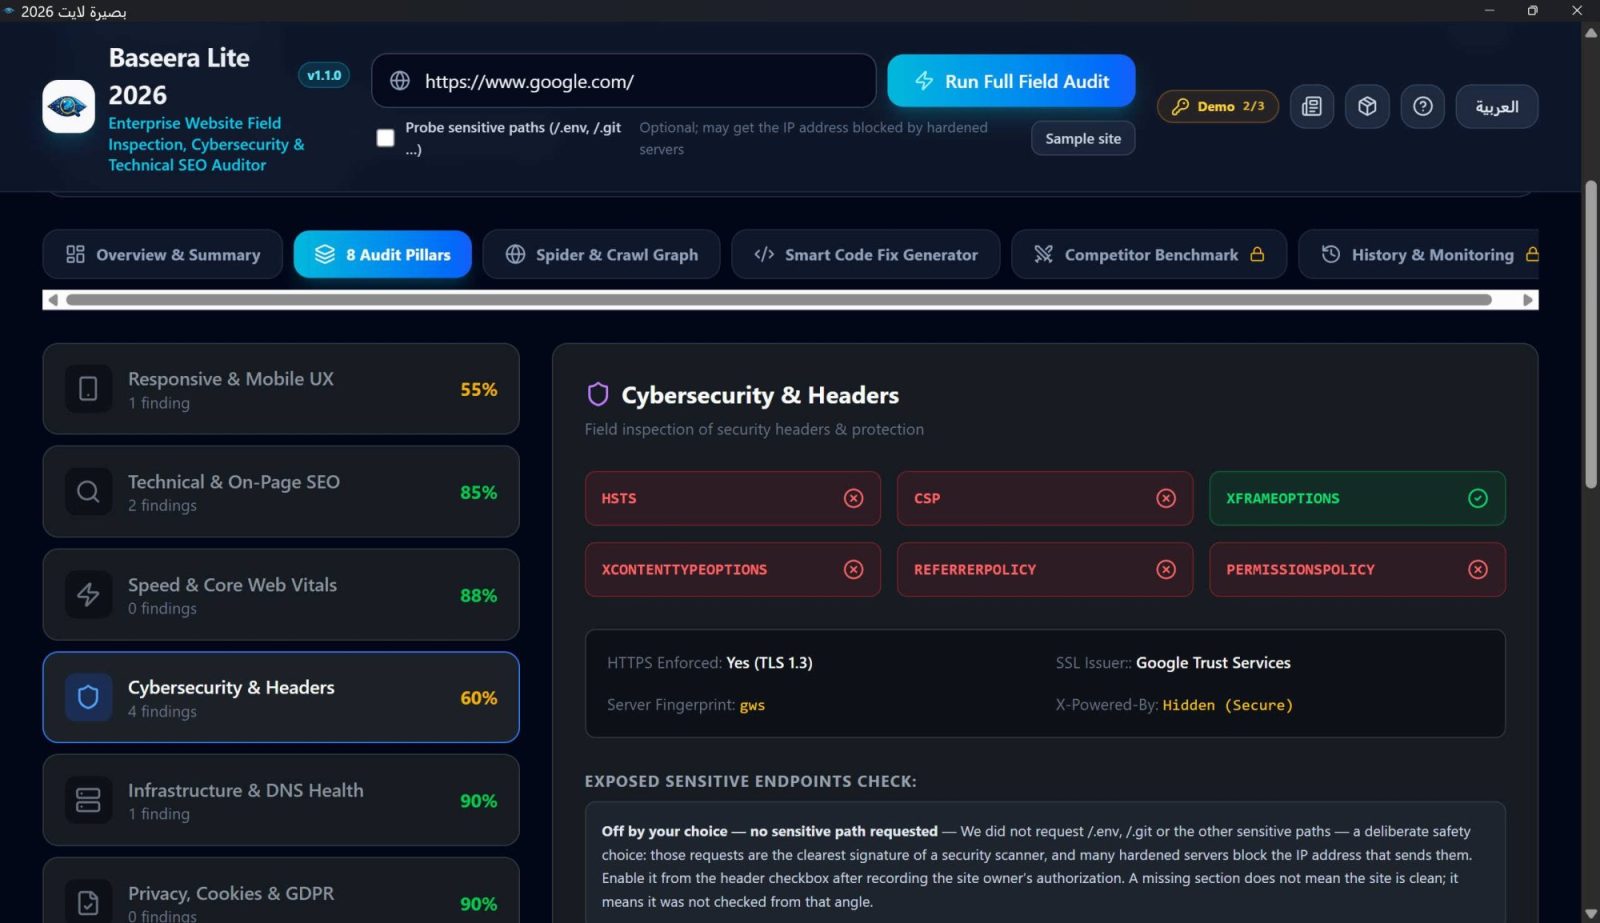
Baseera Lite 2026 is a complete field-inspection suite for cybersecurity and technical SEO. Running natively on Windows, it examines your website the way an independent expert would: eight pillars covering responsiveness, technical SEO, performance, security, infrastructure, compliance, accessibility, and a real crawler that browses your pages rather than stopping at the homepage. Each pillar gets its own score and full detail, and everything converges into one bilingual, exportable report plus a fix generator with copy-paste-ready code for Nginx, Apache, WordPress, meta tags and JSON-LD schema.
Its philosophy is honesty before polish. Every number in the report is genuinely measured; anything that could not be measured is stated plainly — “not measured”, “not retrieved” — instead of being invented, and a hosting provider is never named without evidence measured from the server's own headers. If your firewall blocks the inspection, the report says so instead of claiming a false all-clear, which is exactly what free web tools do when they return “everything is fine” about a site they never actually reached.
Crawling is as polite as it is thorough: a declared identity, realistic timeouts, full respect for 429 responses and rate limits, and a guard that keeps the audit away from private internal networks. Probing sensitive paths is opt-in, off by default, and gated behind your written acknowledgement that you are authorised to test the target — no firewall bypass and no evasion, because compliance comes before capability.
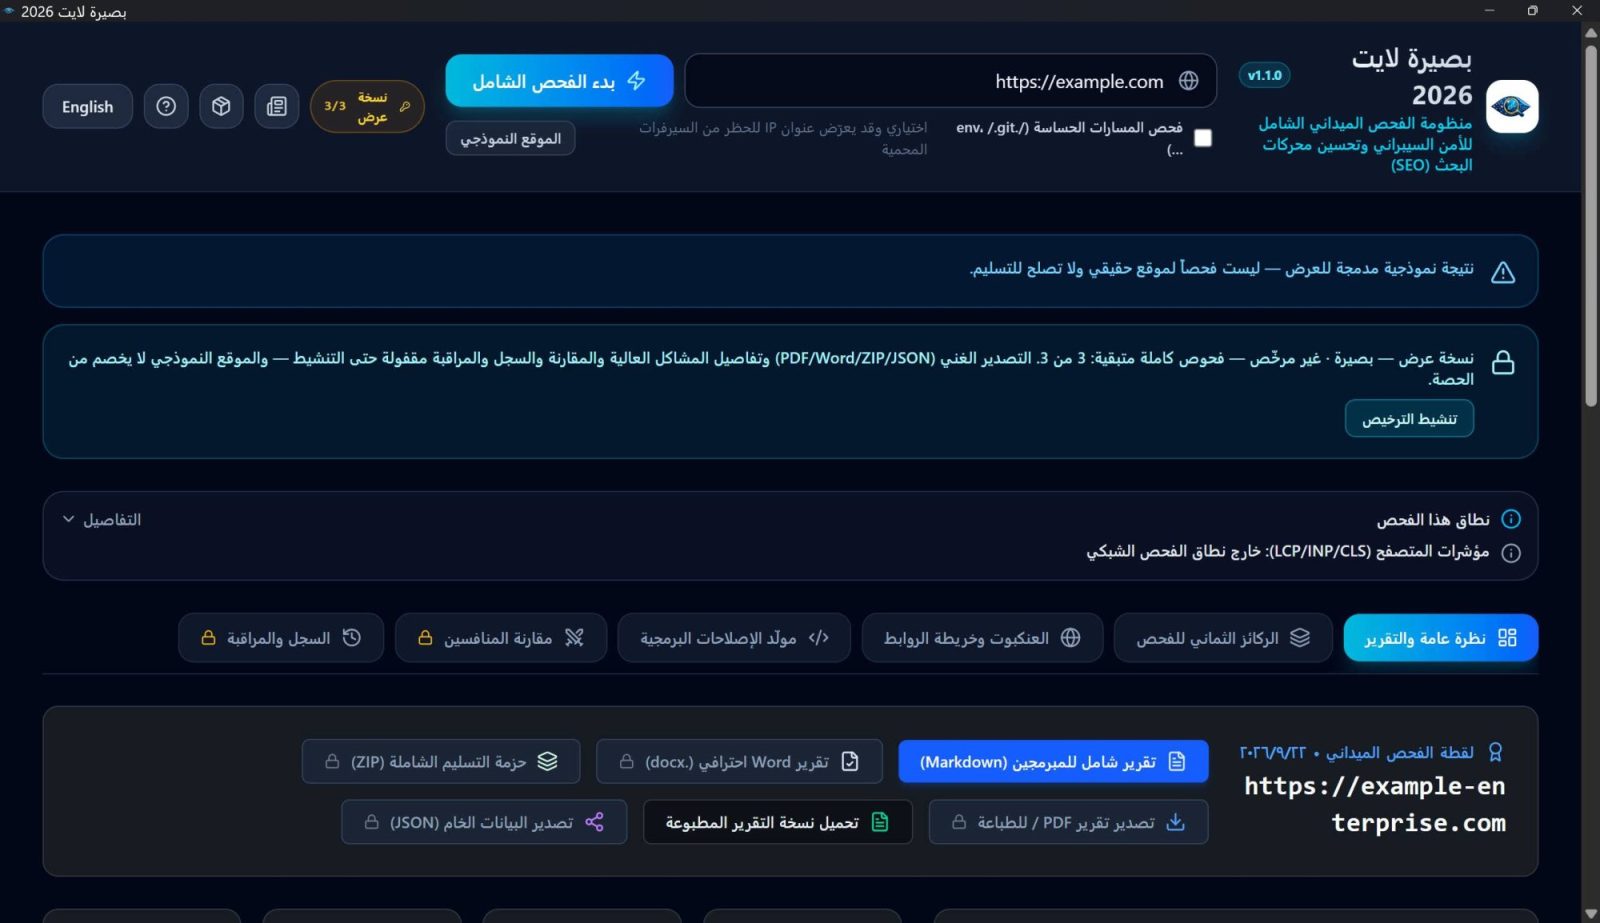
Trying it carries no risk. A permanent demo with no expiry date grants three full scans on your device — measured by quota, not by the calendar — and quota is only spent on a scan that actually completed; a failed or blocked audit is free. Alongside it sits a complete multi-page sample site bundled inside the app, built with deliberate faults (an exposed .env file, a Cloudflare-style blocked page, a rate-limited 429 route) so you can watch the tool work against a real target offline and without spending quota. The seven demo locks are visible, never hidden: every locked feature stays on screen with its name, the reason it is locked and an activation button — no silent walls, no surprises.
Your data stays with you: no account, no cloud, and no third party ever receives your URL or your reports. Audit history and scheduled monitoring are stored locally on your machine, and licensing itself works offline — activation is bound to your device fingerprint and signed with Ed25519. The key request is sent in one click over WhatsApp or email, already carrying the app name, its version, your device code and, if you like, your name and phone number, so you never have to explain anything.
Baseera Lite is the lightest member of the Baseera family: no server, no cloud subscription, built for the site owner and the small agency that need honest, deliverable field evidence before and after a contract. Next to the audit sit scheduled monitoring that re-runs the scan automatically and warns you of degradation or outage before your clients notice, and a field comparison of up to three competitor sites in the same session with a pillar-by-pillar table.
New Release
Version 1.1.7 Windows 10/11 (64-bit)
Baseera Lite 2026
Baseera Lite 2026
Field-grade cybersecurity & technical SEO audits with honest reports, fully offline
App screenshots
See the app
A quick look inside — 11 screenshots available
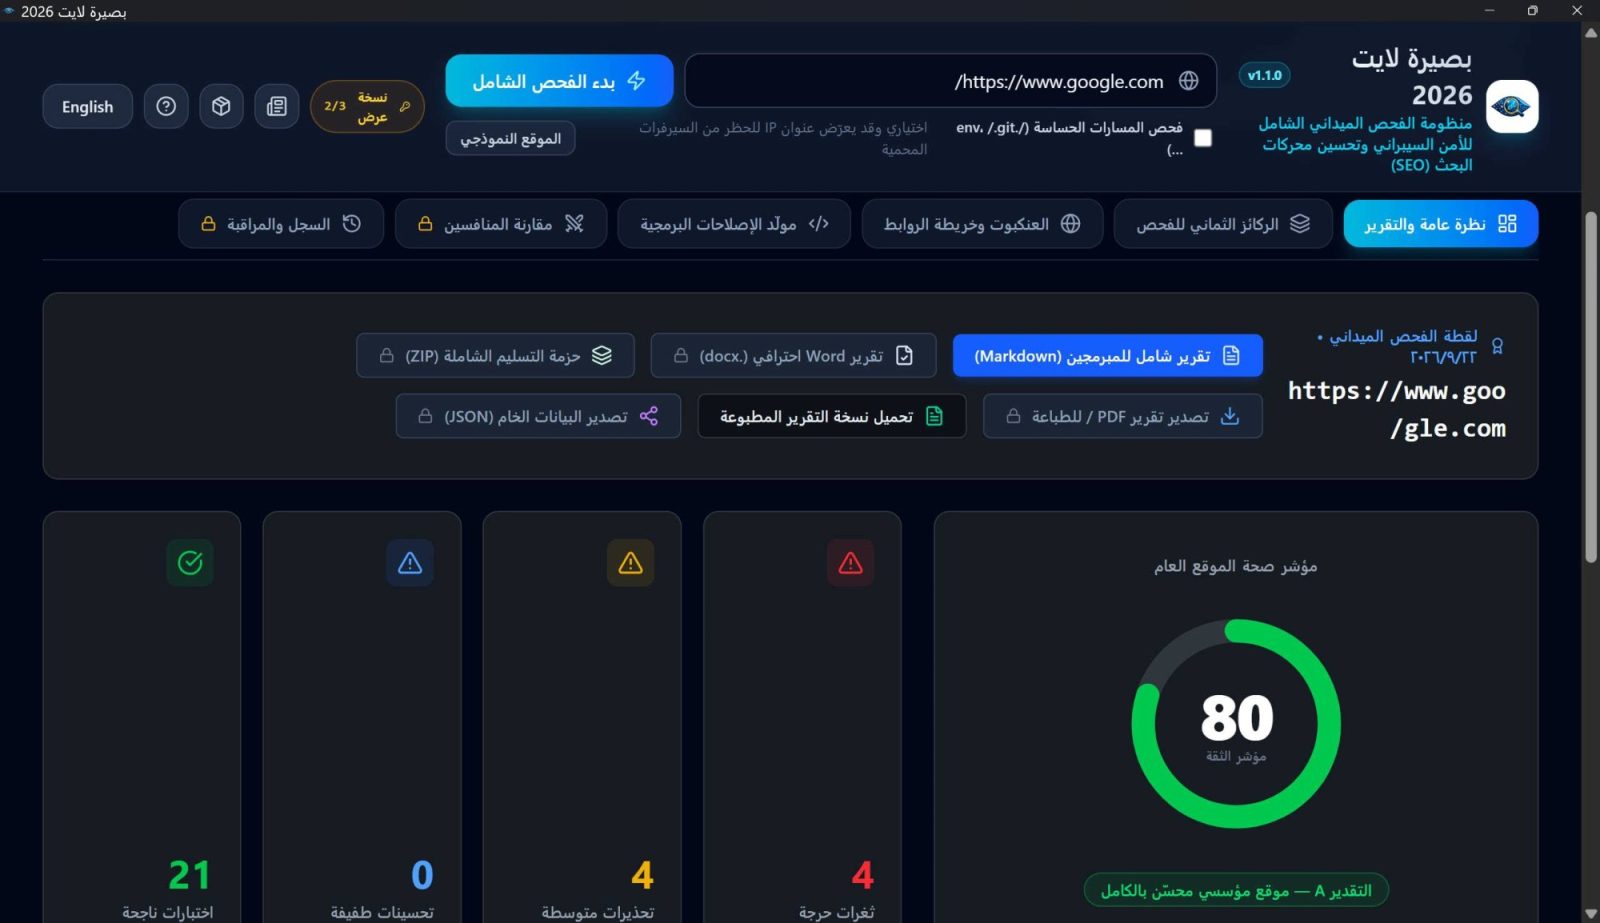
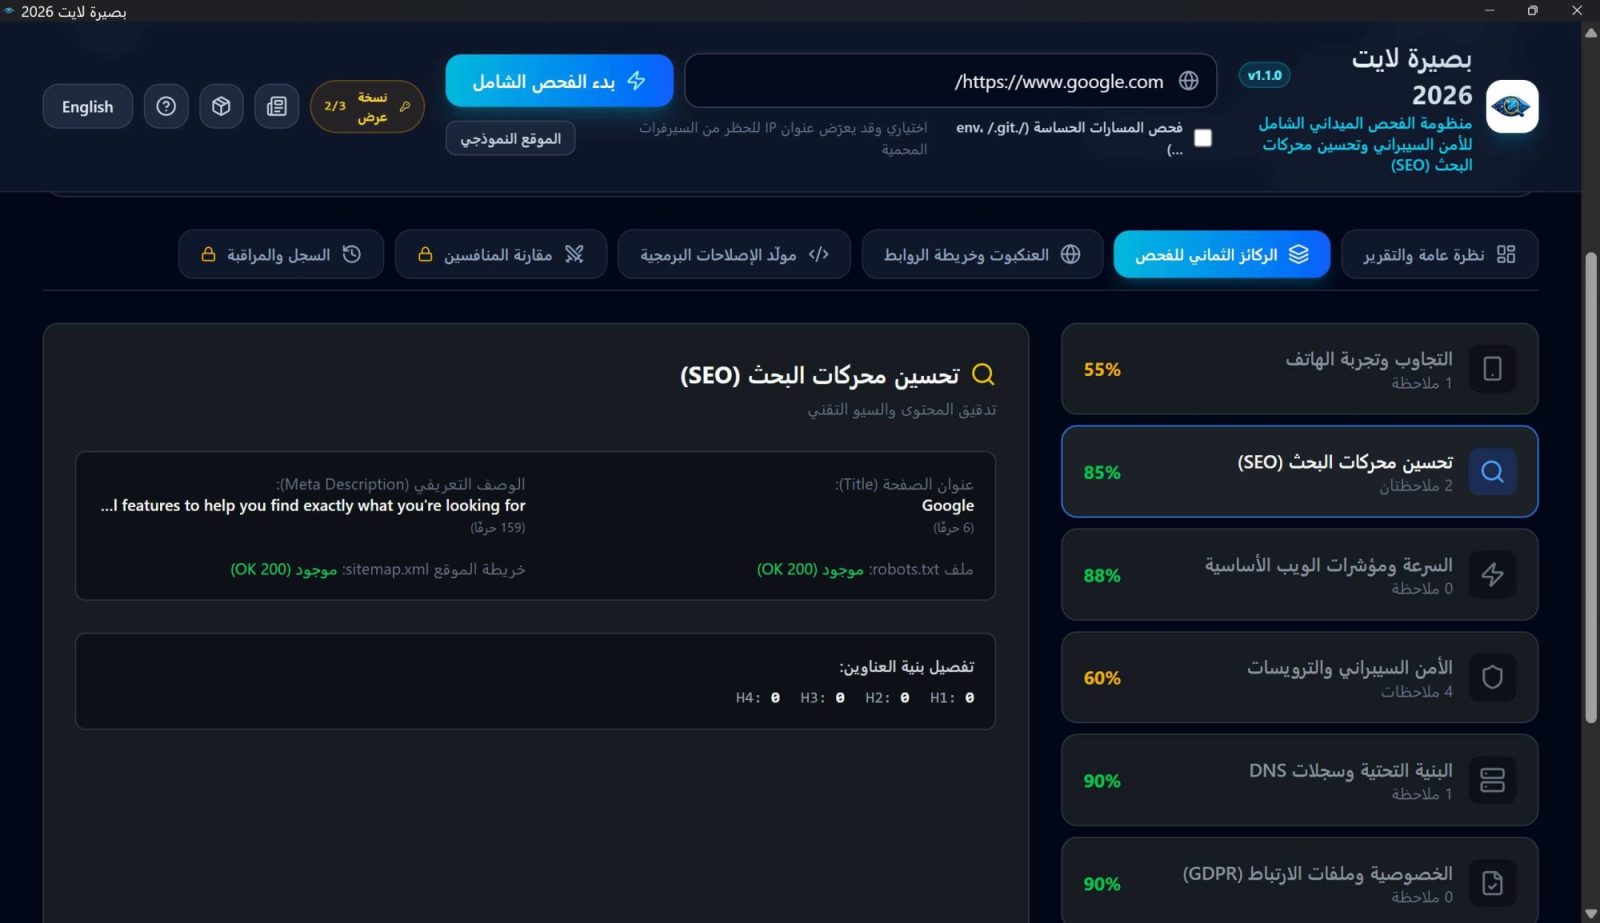
About the app
What does Baseera Lite 2026 do?
The problem it solves
Site owners cannot see their websites the way search engines and security scanners do. Free web tools ask you to hand your URL to third-party servers and return shallow, generic verdicts, while a firewall-protected server simply blocks them — so they come back with a misleading “everything is fine” about a site they never reached. The professional alternatives are either expensive monthly cloud subscriptions, or command-line tools that assume security expertise, or a human auditor with cost and delay attached. The result: exposed faults (a public .env file, missing security headers, a certificate near expiry, a domain about to lapse) and technical SEO defects that live for months before anyone notices — and are usually discovered after the breach or after the rankings fall.
Who is this app for?
Small and medium business owners who run their own sites; marketing and SEO agencies that need evidence they can hand to a client; developers and freelancers who take over websites and want them audited before and after delivery; technical support and operations teams; and security or compliance auditors across the Arab region. It fits especially well where connectivity is unreliable, or where policy forbids uploading client data to external cloud services.
Key features
- 🧭 Eight-pillar field audit — responsiveness, technical SEO, performance, security, infrastructure, compliance, accessibility and crawling, each scored and detailed in one report.
- ✅ Honesty before polish — no invented figures: anything unmeasurable prints as “not measured” or “not retrieved”, and a blocking server is disclosed, never hidden behind an all-clear.
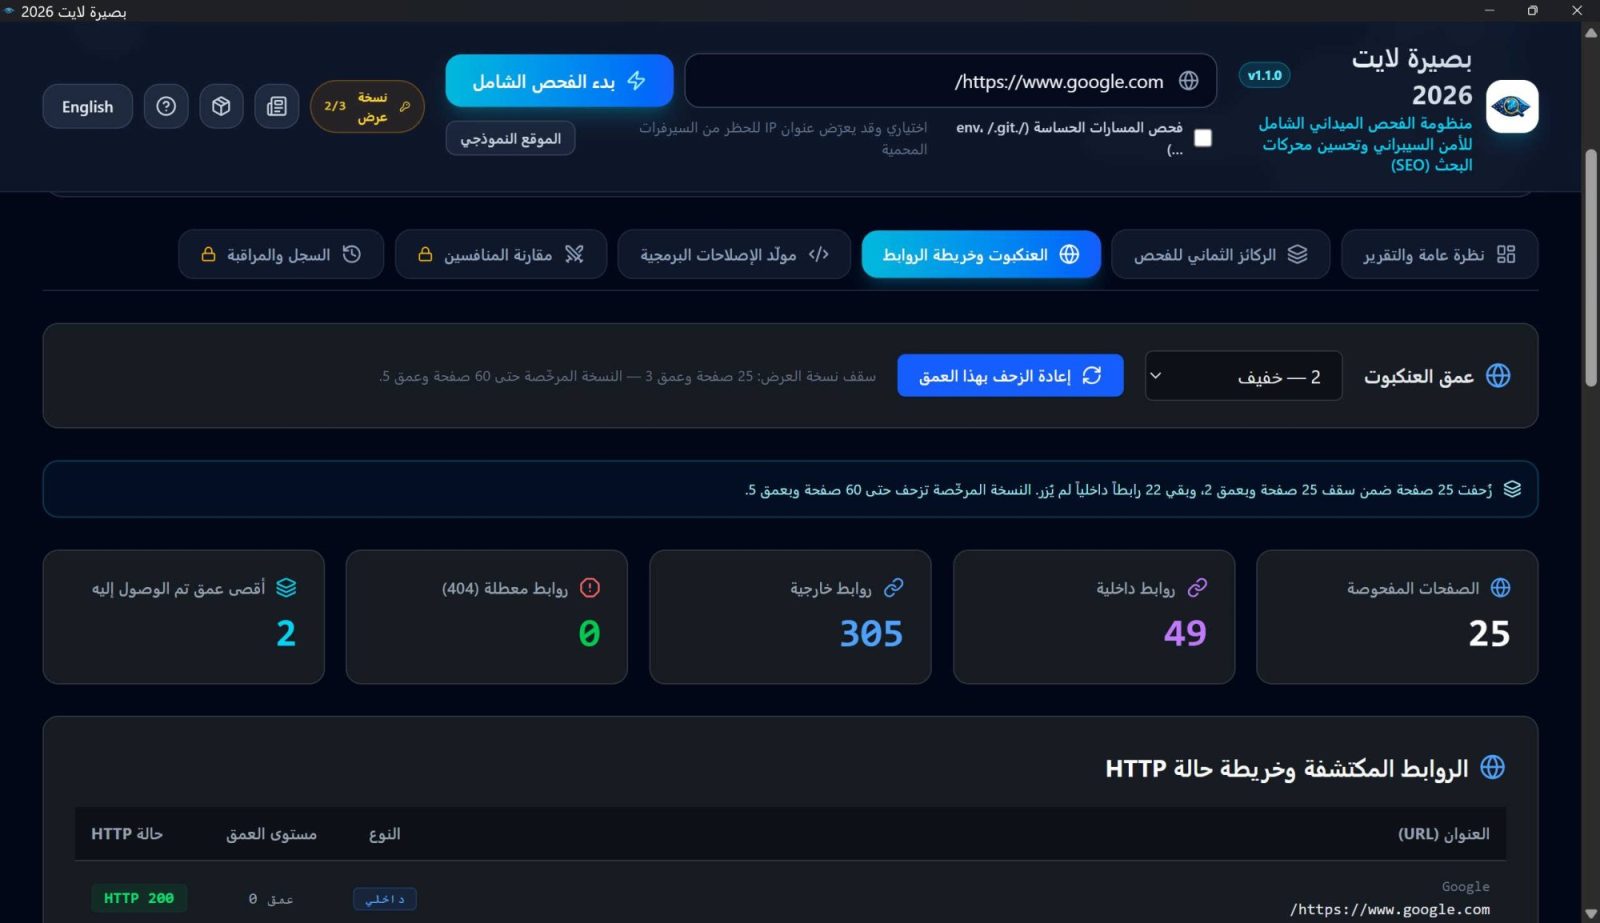
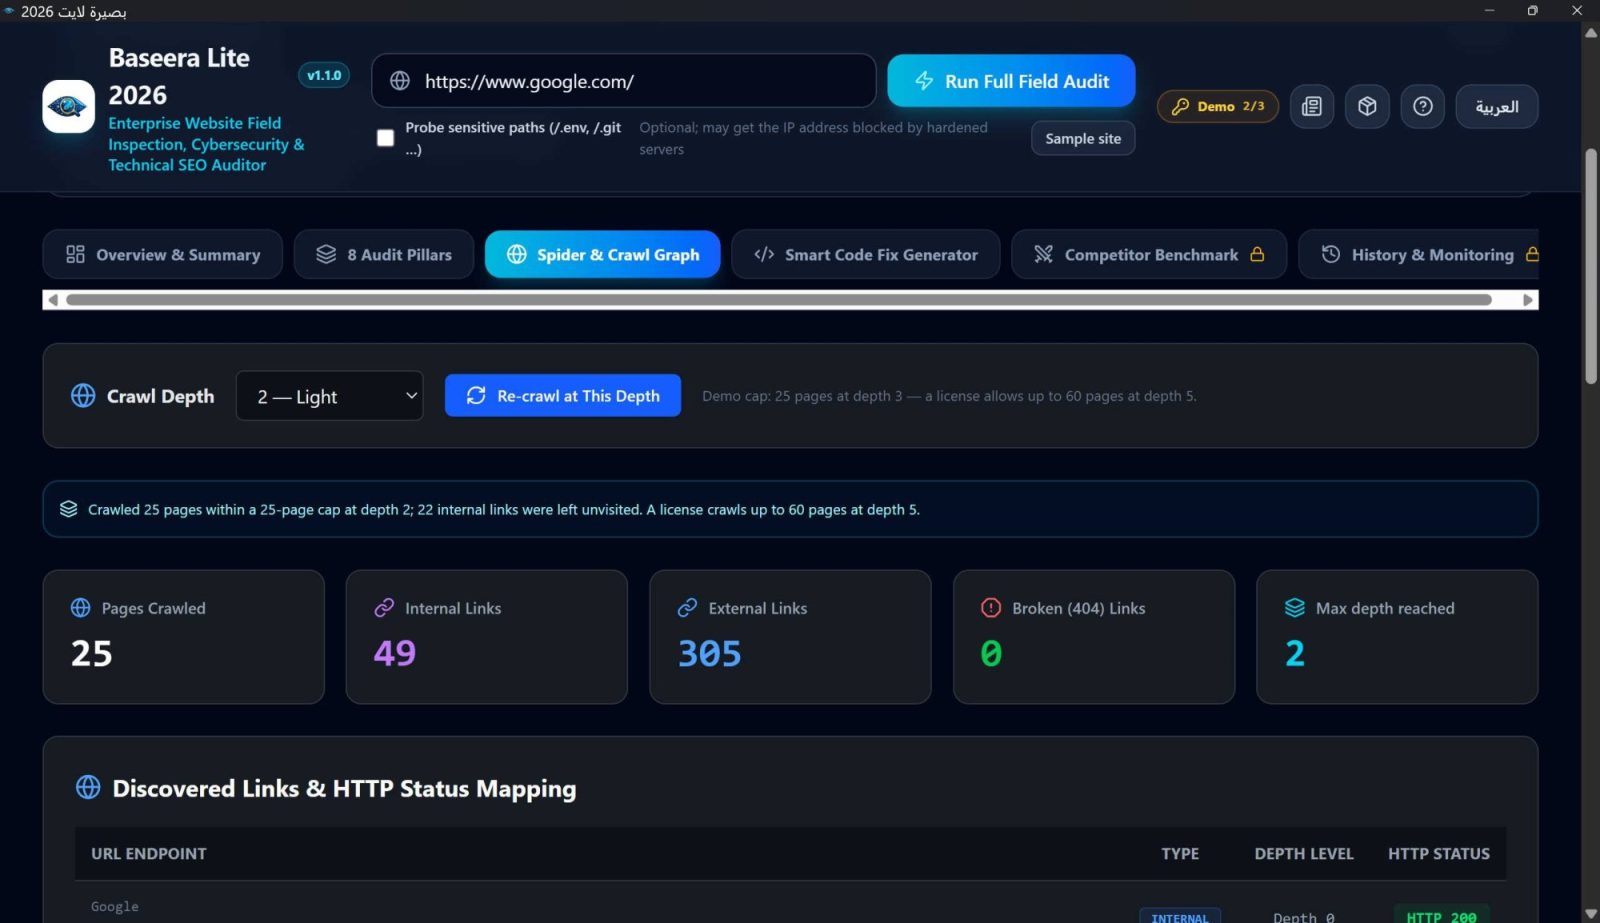
- 🕷️ True multi-page crawler — browses your pages at an adjustable depth from 1 to 5 (up to 58 pages on a license, 25 pages at depth 3 in the demo), finds orphan pages and dead links, and honestly reports how many pages went unvisited when it reaches its cap.
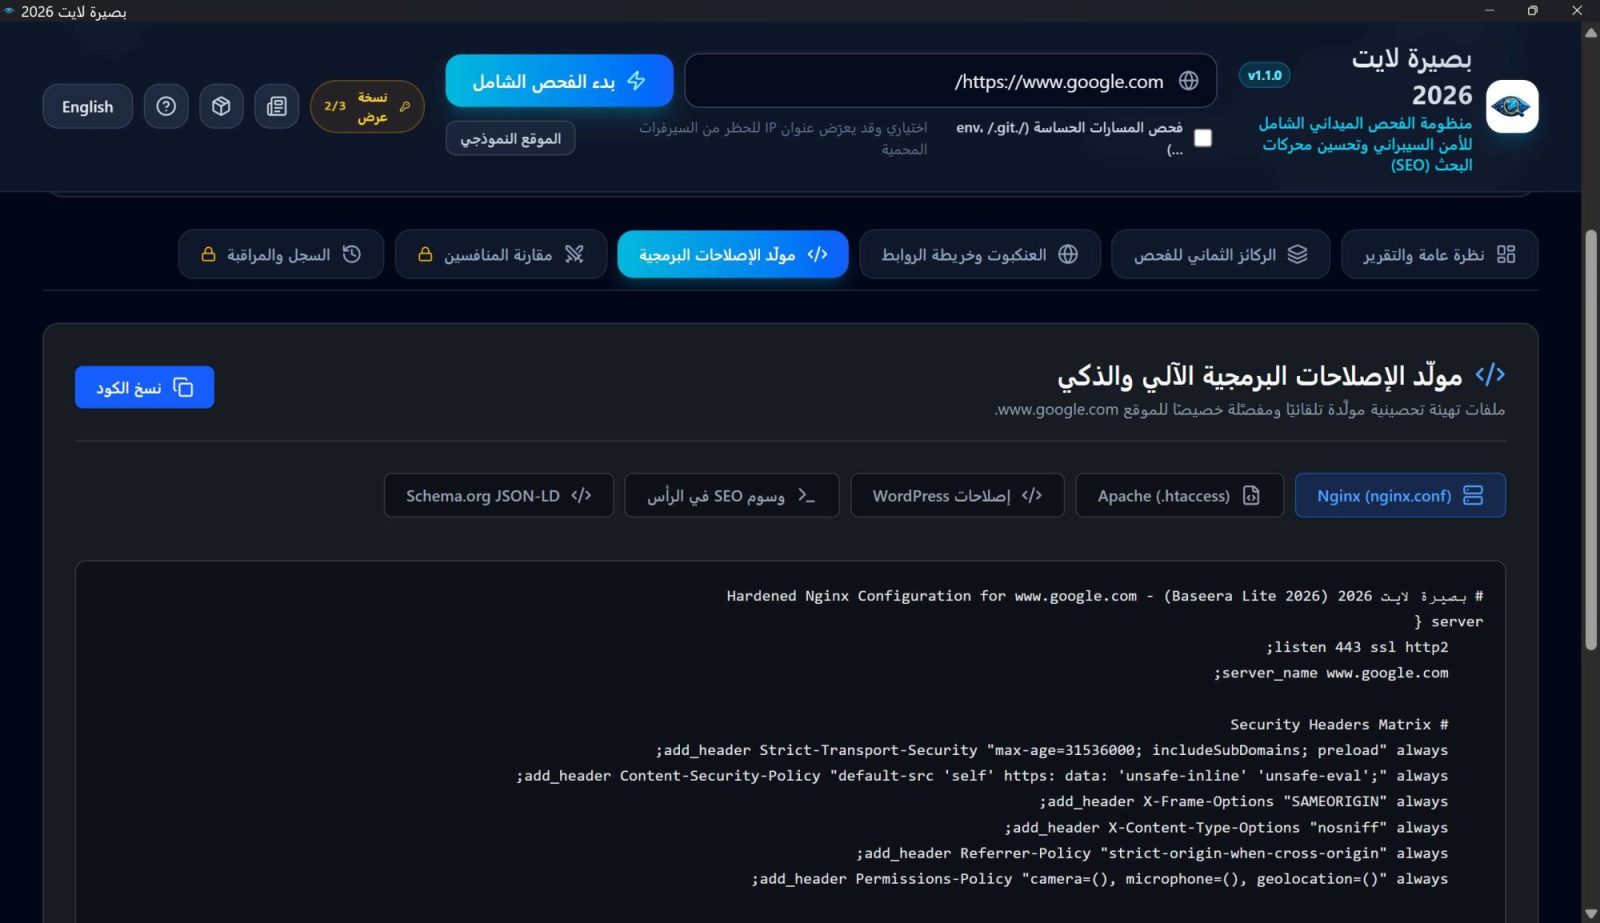
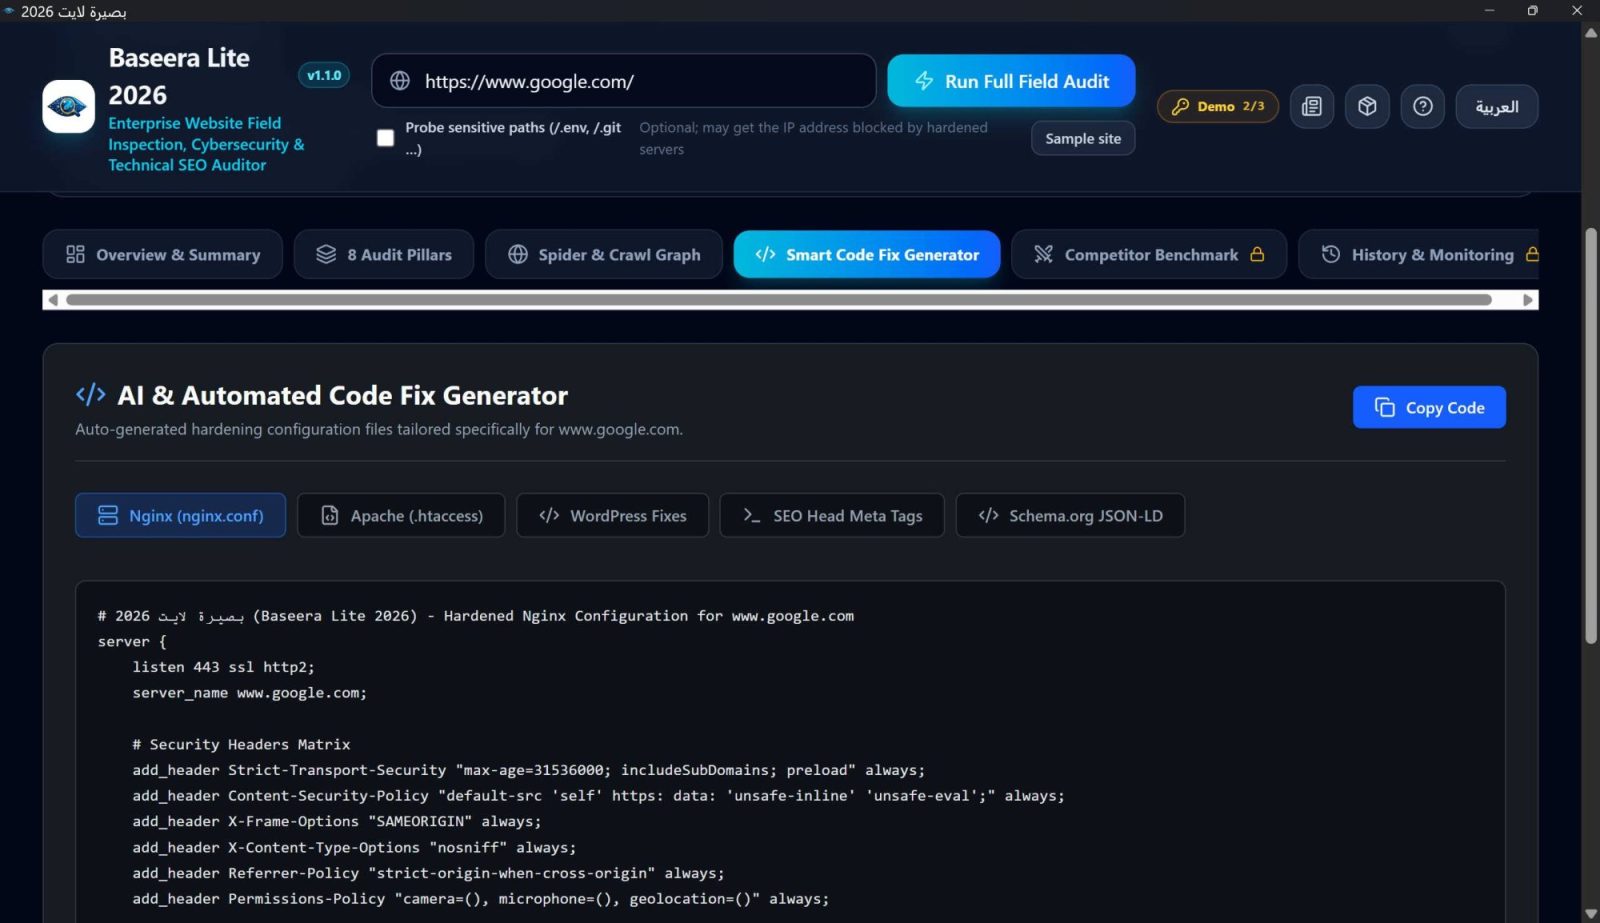
- 🛠️ Fix-code generator — five copy-paste vaults: a hardened Nginx config, an Apache .htaccess, WordPress (wp-config and functions), head meta tags and JSON-LD schema, all built from your own findings.
- 🤝 Polite crawling that won't get you blocked — a declared identity, realistic timeouts and full respect for 429 responses and rate limits, so an audit never gets your address banned.
- 🔐 Authorization gate for sensitive paths — sensitive-path probing is opt-in behind your written acknowledgement: no firewall bypass, no evasion — compliance before capability.
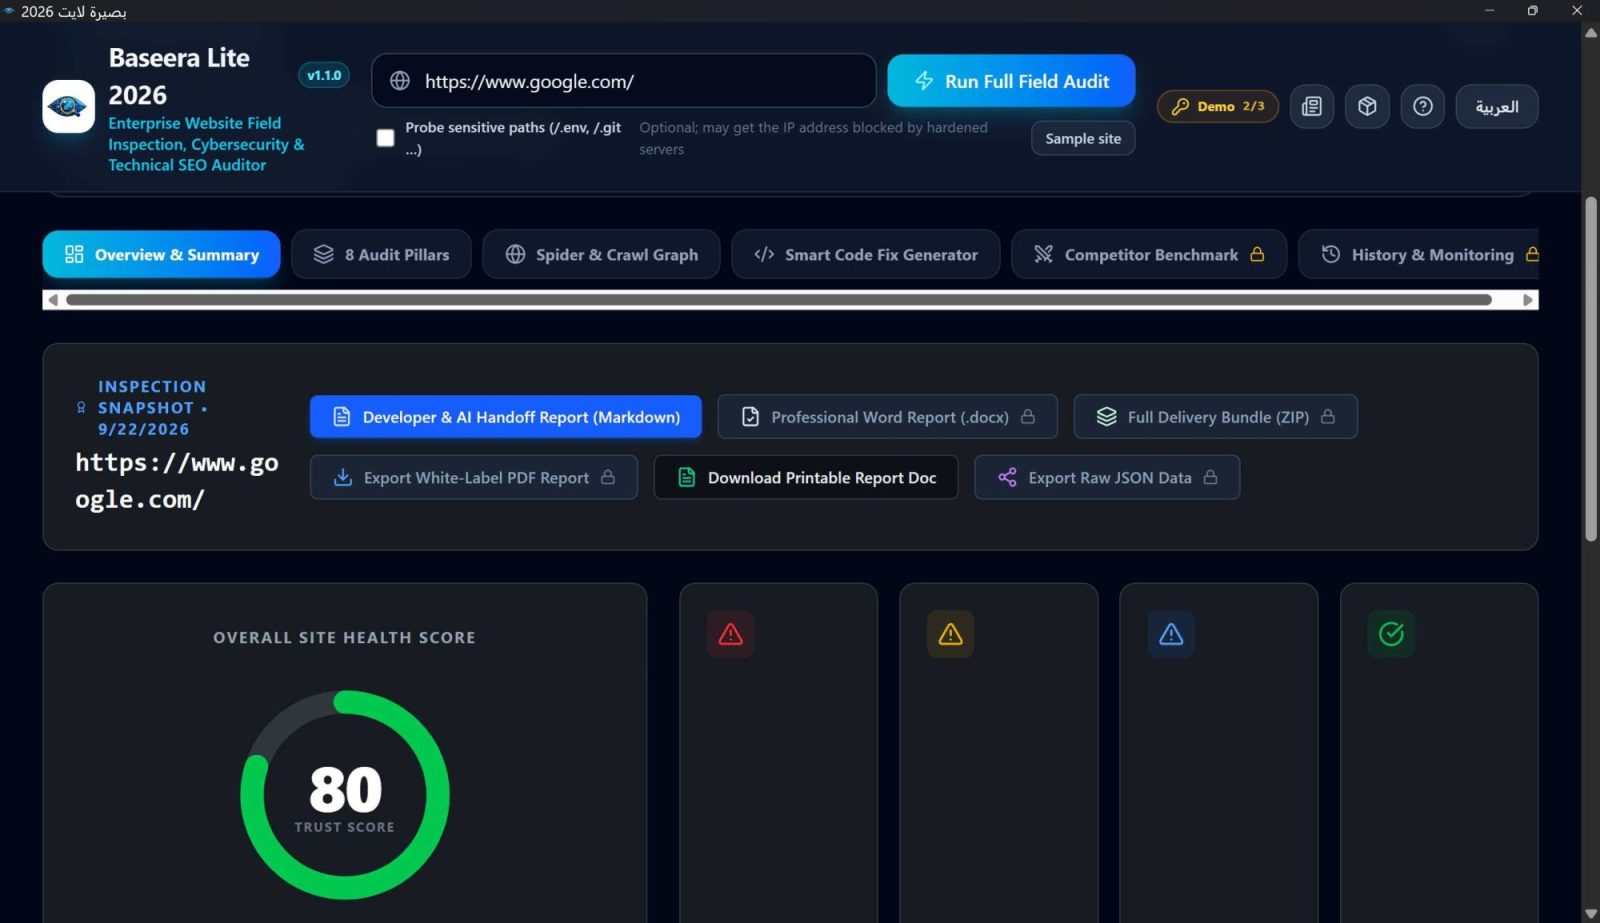
- 📄 Bilingual exportable report — Markdown and HTML for everyone, plus PDF, Word, JSON and a full delivery bundle (ZIP) for licensees, ready to hand over as-is.
- 📜 Registry data as the registry states it — an RDAP card with registration, expiry and DNSSEC status; if the registry stays silent it prints “not retrieved” instead of guessing, and warns before expiry.
- ⏰ Scheduled monitoring that warns first — re-run the audit automatically on a schedule and catch degradation or outage before your clients do, with a stored result history per run.
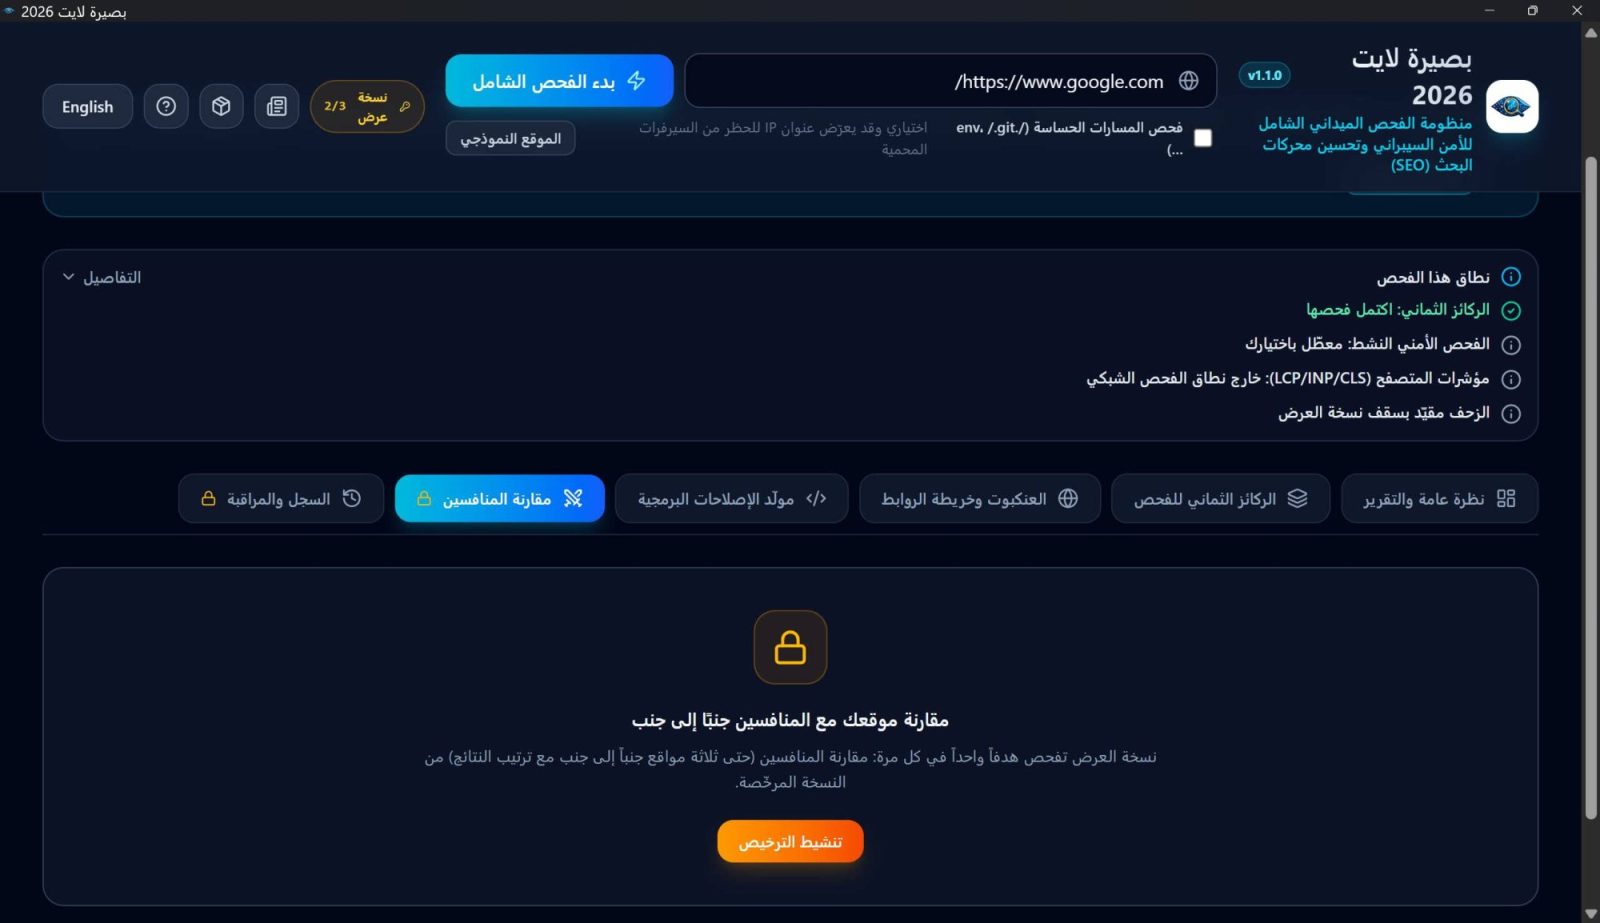
- ⚔️ Field comparison against competitors — audit up to three competitor sites alongside yours in one session, with a pillar-by-pillar table showing where you lead and where you lag.
- 🧪 Built-in sample site for a real trial — a multi-page site bundled in the app with deliberate faults (exposed .env, blocked page, 429 route) so you can watch it work on a real target, offline and quota-free.
- ⏳ A demo that never expires — three full scans per device, measured by quota rather than time, with locks shown by name, reason and activation button: no surprises, no silent walls.
- 🔑 Device-bound licensing, no server — Ed25519-signed activation that works offline, with the key request sent in one click over WhatsApp or email carrying the app name, version and your device code.
- 🔒 Your data stays on your machine — no account, no cloud, and no third party ever receives your URL; it runs without stable connectivity and keeps its history and monitors locally.
- 🧾 A three-state verdict: blocked is not safe — Every audit ends with a declared outcome — complete, partial or blocked — with measured reasons in both languages. If protection stops the audit halfway, the report says so instead of claiming false safety.
- 🛡️ A private-network guard — It refuses internal addresses and localhost, and is re-checked at every redirect hop, so a public address that redirects inward cannot fool it.
- 📋 A scope statement separating “not requested” from “failed” — The report separates a genuine warning from a scope statement: a probe switched off on purpose, a metric a static audit cannot measure, or a ceiling imposed by the licence tier — so your choices are never read as tool failures.
- 🎯 An overall score, a grade and an executive summary — A score out of 100 with a three-level grade (A ≥ 80, B ≥ 55, C below), an independent score per pillar, and an executive summary naming the high-severity count and the order of work.
- 🔐 The certificate, exactly as it declares itself — Certificate validity, days remaining, issuer and transport protocol — and when verification fails it prints “not retrieved” and is never translated into “healthy”.
- 💼 A portable edition: no install, no administrator rights — A compressed bundle holding the executable, a marker file beside it and an instructions file: unpack it and run it from its folder, and your reports and history stay in a data folder alongside — suited to an external drive or a client's machine.
- 🧩 A written recommendation for each of the 29 finding types — Every one of the 29 finding types carries a recommendation in Arabic and English, and 18 of them carry a snippet ready to paste into the right place on your server or pages.
Requirements
Windows 10 or 11 (64-bit) · WebView2 runtime (preinstalled on Windows 11 and most Windows 10 systems; the installer fetches it if missing) · 1024×700 minimum resolution · auditing requires reaching the target site; the interface and reports open offline.
Licensing
Paid — a permanent three-scan demo, then a signed licence for your device that works offline.
Related apps
You may also need
 Directly compared with this app
Baseera Pro 2026
A nine-pillar audit of your website — measured, not guessed. View app
 From the Codext suite
Saloni Pro 2026
Your entire salon on one screen — it works even without the internet. View app
 From the Codext suite
Khadamati Pro 2026
One smart ledger for your customers, services, payments and tasks — with WhatsApp invoices and reminders in a click. View app
App screenshots
See the app
11 screenshots
Version history
Versions & updates
v1.1.7
Download
05 Nov 2026
A corrective release: the in-app text now states a 58-page crawl ceiling instead of 60, and support hours are 11:00 to 19:00 Damascus time instead of 09:00 to 21:00. No change to the audit engine or the eight pillars.
Pricing Plans
Choose Your Plan
Permanent Demo
$0
Three full scans per device — no expiry date, no credit card. Every lock is shown by name and reason.
Download the Demo Edition
FAQ
Frequently asked questions about the app
Yes, but it is not a time-based trial: a permanent demo with no expiry date grants every device three full scans of real targets, plus an unlimited built-in sample site that costs no quota, so you can exercise the whole tool offline.
The app does not lock up and nothing is deleted. Starting a new scan on a real target stops, with a notice explaining why and how to activate; the bundled sample site stays free and unlimited, and every locked feature remains visible with its name and reason.
Because the value here is a report you extract, not data accumulating inside the app. A timed trial would allow unlimited free extraction while it lasts, so we use a fixed per-device scan quota stored in the a location reinstalling cannot reset (mirrored in the data folder), which reinstalling cannot reset.
The app itself needs no server, no account and no cloud: the interface, report, exports and licensing are all local, and activation is verified offline. Auditing a real website inherently requires reaching that website. The bundled sample site works fully offline. Automatic updates are optional and do need connectivity.
No. Requests go straight from your machine to the site you audit (and to the RDAP registry when reading the domain card). No middleman, no account, no report upload. History and monitors are stored locally.
No, deliberately. A private-network guard rejects internal addresses (such as 192.168.x, 10.x and localhost), because probing them from a publicly distributed tool resembles hostile scanner behaviour. The guard judges documentation ranges at /24 precision so genuine public addresses are not wrongly refused.
Windows 10 or 11, 64-bit, with the WebView2 Runtime (preinstalled on Windows 11 and most Windows 10 systems; the installer fetches it if missing). The installer is about 4.5 MB, the portable ZIP about 5.9 MB, and about 60 MB of free disk space is enough. The app itself needs no server and no account; connectivity is required only to reach the site you audit.
Yes. You receive a ZIP archive holding the executable, an empty portable.flag beside it and a readme: extract it and run the app from that folder, and your reports, history and settings are kept in a Data folder next to it — no installation, no administrator rights, ideal for a USB drive or a client machine. Keep the executable and portable.flag together, or the app behaves like an installed copy and stores its data in %APPDATA%. In the interest of precision: license and demo-quota counters still live in the current Windows user's registry (mirrored in Data) for tamper resistance, so a portable and an installed copy under the same Windows account share one quota; full isolation means another Windows account or another machine.
The customer opens the activation window, sees their device code (16 characters as XXXX-XXXX-XXXX-XXXX) and presses one button to build a complete request carrying the app name, version, device code and their own name and phone (entered once, remembered after). It is sent over WhatsApp or email, or copied as text. The company issues a signed key bound to that device; the customer pastes it and the license takes effect immediately, offline, with no account.
Payment channels are not handled inside the app itself. To arrange payment and receive your activation key, contact the company via WhatsApp +963 995 408 915 or info@codextsoft.com; we will arrange the most convenient method for you and then send the signed key for your device.
Updates are included for the duration of an active license — indefinitely for the lifetime license — and arrive through the app's own signed update channel without reinstalling. Locked features unlock the moment you activate, with nothing extra to download.
No. Baseera Lite is the lighter member of the family: no server, no cloud subscription, with crawl caps and a feature set sized for a site owner or a small agency. Anyone needing deeper audit depth and broader workflows belongs on Baseera Pro.
Ready to get started?
Apps and their updates are managed on ProgixSoft — go to the app page to continue.
Download the Demo Edition